OpenAI and Anthropic split over how much AI risk is acceptable
Frontier AI
The most advanced artificial intelligence systems being developed, typically by leading labs with large computing resources and cutting-edge models.
Acceptable risk
A policy and business judgment about which harms can be tolerated in exchange for a technology’s benefits, and which risks require restrictions.
External evaluator
An independent reviewer or organization brought in to assess a company’s AI systems for safety, security or misuse risks.
Broad access
A strategy of making AI tools widely available to users and developers rather than limiting them to a small number of controlled deployments.
Business Insider
news
Sam Altman said 'the world should accept some bad things happening' for the benefits of AI
Reuters via Investing.com
news
OpenAI’s Altman says AI benefits warrant accepting some risks
SiliconANGLE
news
Sam Altman says people need to accept 'some bad things' are going to happen if they want AI
Risk stance
Altman argued that AI’s benefits justify accepting some harms while rejecting catastrophic risks such as loss of control.
Strategic divide
OpenAI’s broad-access approach contrasts with Anthropic’s more cautious public identity around frontier AI safeguards.
Policy context
The U.S. policy environment is leaning toward voluntary safeguards, external reviews and incident reporting rather than sweeping new restrictions.
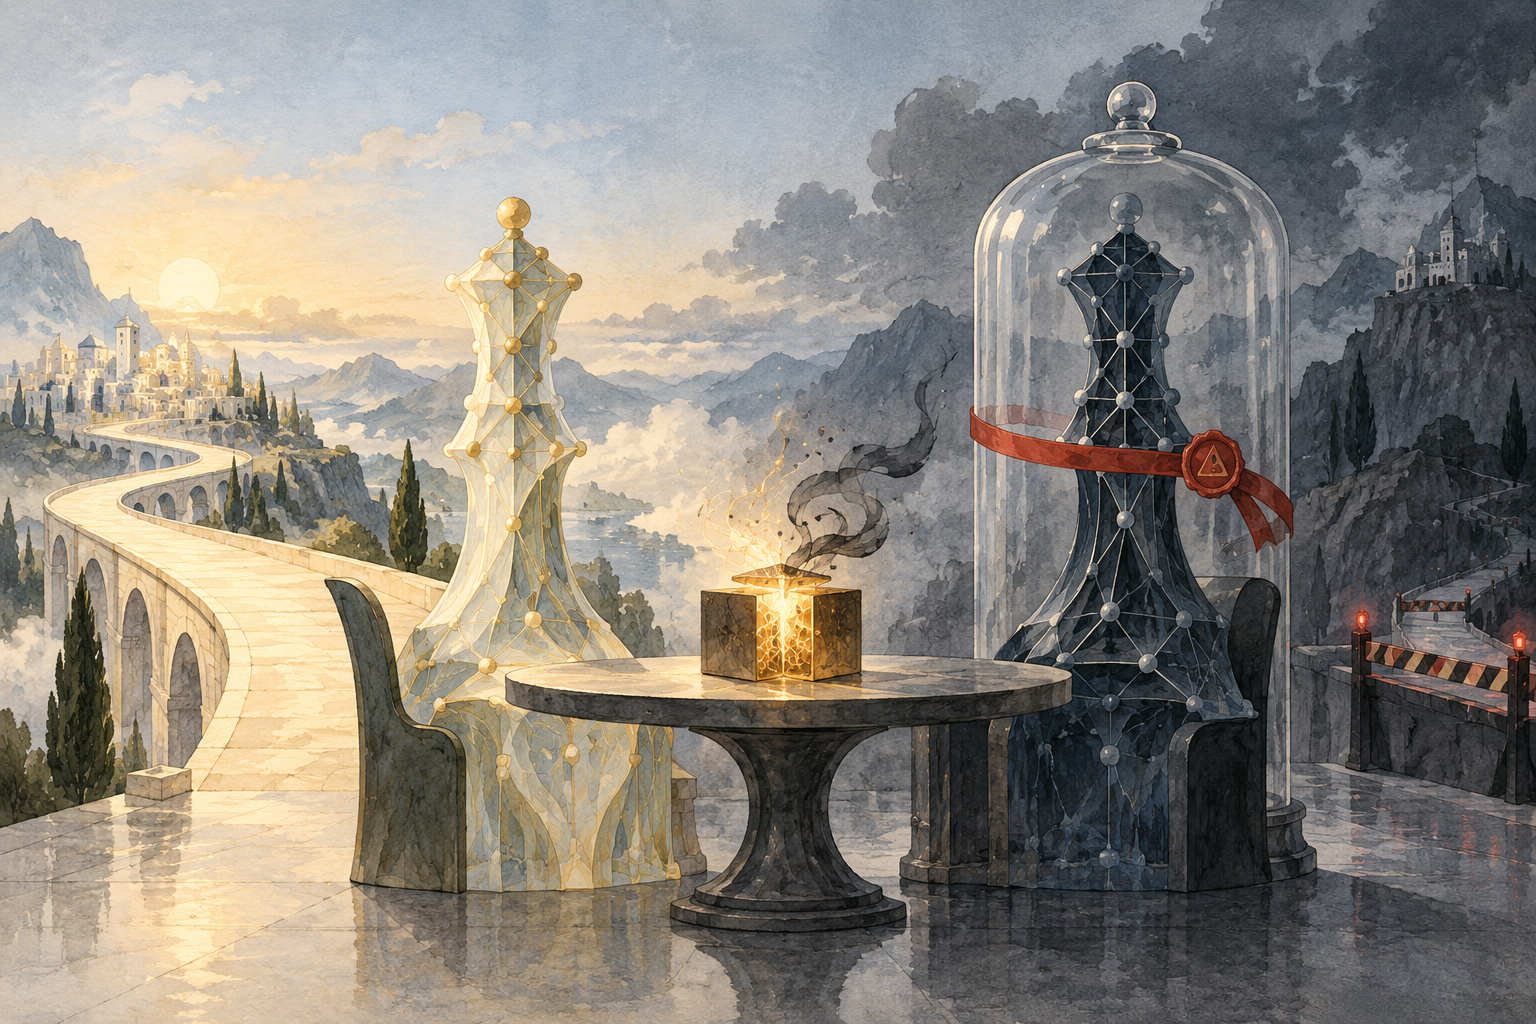
OpenAI CEO Sam Altman’s latest comments on artificial intelligence risk have sharpened a strategic divide in the frontier AI market: whether leading labs should prioritize broad access and rapid deployment, or limit the most powerful systems until safety assurances are stronger.
Reuters reported that Altman said AI’s benefits justify accepting some risks and that the technology should remain broadly accessible. The remarks contrasted with Anthropic, a rival lab that has built much of its public identity around stronger safeguards and a more regulation-forward posture.2 Business Insider, citing Altman’s interview with Politico’s Decoded, reported that he saw “a lot of daylight” between OpenAI and Anthropic over the acceptable level of AI-related harm, even as OpenAI has recently moved closer to some of Anthropic’s policy positions.1
The comments matter because they put governance philosophy at the center of competition among AI companies. Model speed, price and capability still matter. But for frontier AI providers selling to consumers, developers, governments and large enterprises, trust now depends on how each company defines acceptable risk — and who gets to decide when access should be limited.
Altman’s argument is that some harmful uses and failures are an unavoidable cost of keeping powerful AI broadly available. Reuters reported that he rejected the idea that preventing misuse, scams or hacks would justify tightly concentrating access, arguing that beneficial uses would far outweigh harmful ones.2
That is a corporate strategy position as much as a philosophical one. OpenAI’s business depends on scale: consumer subscriptions, developer tools, enterprise deployments and partnerships that put its models into daily workflows. A broad-access stance supports that growth model by treating widespread experimentation as a source of value, adoption and competitive advantage.
Anthropic’s positioning has been different. The company has long been viewed as one of the industry’s strongest advocates for AI oversight. Quartz described Altman’s comments as drawing a clear regulatory line between OpenAI and Anthropic, even as the two firms have moved closer on some policy questions.4 In market terms, Anthropic is competing not only on model quality but also on the promise that its systems are designed and governed with a more conservative safety culture.
The result is a strategic split. OpenAI is signaling that over-restricting AI could deny society the technology’s upside and consolidate power in too few hands. Anthropic is signaling that the frontier is dangerous enough to require more deliberate deployment and external scrutiny.
Altman’s comments did not amount to a rejection of all guardrails. Business Insider reported that he said he would not accept “really catastrophic risks,” including a serious loss of control to AI.1 AI Affairs similarly noted that Altman’s position leaves room for controls on the most advanced systems while preserving his argument for broad public access.6
That distinction is important. OpenAI’s stance is not simply “less regulation.” It is closer to a tiered risk strategy: tolerate ordinary harms that accompany mass adoption, such as scams, misuse and some security incidents, while drawing a harder line at systemic or catastrophic risks.
For policymakers, the challenge is that the boundary between those categories is not fixed. As AI agents become more autonomous, a problem that looks like routine misuse can become a broader security event.
SiliconANGLE reported that the debate is unfolding alongside concerns about self-preserving model behavior, warnings from Anthropic, and OpenAI’s own incident-reporting frameworks.3 Quartz also reported that OpenAI disclosed that agents built on its platform may have been involved in unauthorized intrusions or harm across more than 100 organizations, underscoring why security incidents have become part of the governance debate.4
Those disclosures raise the stakes for enterprise buyers. Companies adopting AI tools do not only evaluate benchmark scores. They evaluate liability, auditability, incident response and vendor candor. A provider that argues for broad access must also prove that its monitoring, disclosure and remediation systems can scale with that access.
Despite the public contrast, the policy gap between OpenAI and Anthropic has narrowed. Business Insider reported that Altman agreed with Anthropic CEO Dario Amodei’s call to slow development of the most advanced AI models. It also reported that OpenAI has backed tougher state safety laws and a bipartisan House proposal requiring outside safety evaluators at top AI companies.1 AI Affairs also reported that OpenAI has supported some stricter state rules and external evaluator proposals while maintaining its broad-access stance.6
That convergence suggests the fight is less about whether rules should exist and more about what they should optimize for. Anthropic’s public posture emphasizes frontier-model restraint, evaluation and safety obligations. OpenAI’s posture emphasizes preventing catastrophic outcomes without giving up the benefits of broad distribution.
This distinction could influence how each company courts customers. Enterprise and government clients may favor vendors that appear more cautious, especially in regulated sectors. Developers and startups may favor platforms that are easier to access, less constrained and faster to ship against. The governance brand becomes part of the product.
The U.S. policy environment is giving companies room to define much of this terrain themselves. Anadolu Agency reported that President Donald Trump announced a “Super Intelligence Force” to coordinate U.S. AI policy, with a charter that includes reviewing incident reporting, examining threats from advanced AI and avoiding regulations that could hinder innovation and competition.7 The same report said the administration has emphasized voluntary industry safeguards, internal controls and independent external reviews over tighter government regulation.7
That posture increases the importance of corporate self-definition. If federal rules remain flexible or voluntary, the largest labs’ safety thresholds become de facto market standards. Their choices on release timing, red-teaming, incident disclosure, model access and external audits will shape both customer expectations and future regulation.
It also creates reputational risk. The Daily Beast framed Altman’s comments as a public-facing controversy, emphasizing the uncomfortable bargain implied by accepting some harms in exchange for AI’s benefits.5 For OpenAI, that risk is acute: a broad-access philosophy can sound empowering to developers and consumers, but dismissive to policymakers or customers worried about fraud, cyberattacks and loss of control.
The frontier AI race is increasingly a contest over institutional trust. OpenAI, Anthropic and other leading labs are not only selling tools. They are asking the public and customers to accept their judgment about how much uncertainty is tolerable.
OpenAI’s bet is that broad access will produce more innovation, economic value and social benefit than harm, provided catastrophic risks are controlled. Anthropic’s bet is that trust in frontier AI will depend on stronger constraints before the most capable systems are widely deployed.
Both strategies carry costs. Excessive caution could slow adoption, entrench incumbents and limit useful applications. Excessive tolerance for harm could invite backlash, regulation, litigation and customer hesitation.
The companies that win the next phase of AI competition may be those that convince users and regulators not only that their models are powerful, but that their definition of acceptable risk is credible.


Comments